
Managing AI risk in the clinical laboratory
The same AI tools that are speeding up diagnosis in the clinical lab are also arming the people trying to break into it
21 Sept 2026Summary
- Clinical laboratories are rapidly adopting AI, cloud technologies, and digital workflows, but these innovations also introduce new cybersecurity, data governance, and compliance challenges that require careful oversight.
- AI is making cyber threats more sophisticated, enabling convincing phishing attacks, voice cloning, deepfakes, and vulnerable AI-generated code that can expose laboratories to security risks.
- Effective governance, software validation, zero-trust security practices, and controlled use of AI tools are essential to help laboratories innovate safely while protecting patient data and operational integrity.
- Successful AI adoption depends on balancing innovation with risk management, ensuring laboratories have the frameworks, oversight, and infrastructure needed to deploy AI and cloud technologies with confidence.
Clinical laboratories are moving faster than ever, adopting cloud infrastructure, artificial intelligence, and remote connectivity at a pace that would have seemed impossible a decade ago. But that speed cuts both ways. The tools that make labs more efficient are also available to the people trying to attack them.
That tension was the focus of a recent SelectScience® webinar, ‘The Digital Lab Leader's Playbook: Navigating Informatics, Innovation, Security, and Compliance.’ Moderated by Lucy Lawrence, the session featured Dr. David McClintock, chair of the Division of Computational Pathology and Informatics in the Department of Laboratory Medicine and Pathology at Mayo Clinic and associate professor at Mayo Clinic College of Medicine and Science. He walked attendees through how cybersecurity threats are evolving alongside AI, how labs should think about cloud adoption, and how to build governance that enables innovation rather than blocking it.
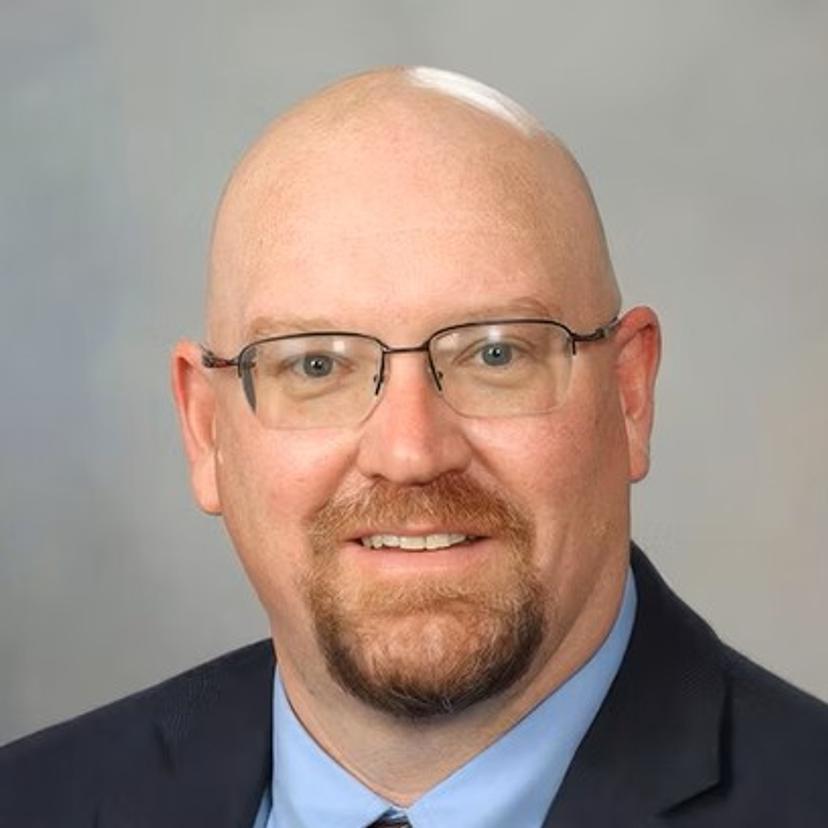
Dr. David McClintock, chair of the division of computational pathology and informatics in the Department of Laboratory Medicine and Pathology at Mayo Clinic and associate professor at Mayo Clinic College of Medicine and Science
AI is making cyberattacks harder to spot
Dr. McClintock opened by reframing the question labs should be asking. "The question as we move forward for this topic really isn't, should labs innovate, adopt AI, and move to the cloud," he said. "But more importantly, it's how do labs transform their practice without becoming the next cybersecurity headline."
Traditional cybersecurity training has worked, he said, noting that human error accounted for about 85% of breaches in 2021 but has since fallen to around 62%. Attackers have shifted toward exploiting software vulnerabilities directly, now involved in roughly 30% of breaches, while social engineering remains the third most common breach pattern, tied to more than 5,300 incidents a year.
What has changed most, he explained, is the sophistication of the attacks that remain. Instead of the clumsy phishing emails many lab professionals have been trained to spot, AI now generates fluent, context-aware messages with no typos or awkward phrasing. He described a growing shift toward smishing and vishing, fake text messages and phone calls built around an urgent, plausible scenario, which he said succeed at a rate 4% higher than traditional email phishing. Some attackers now use voice cloning or deepfake video to impersonate a colleague or executive. "The bottom line here is that while our cybersecurity training is helping, the threats that are evolving using AI are getting really, really sophisticated," he said.
AI-generated code is creating new security gaps
One newer risk involves labs and vendors using AI tools to write their own software, a practice sometimes called vibe coding. Dr. McClintock explained that AI-generated code is "routinely vulnerable across every major tool," citing research showing that 62% of AI-built applications ship with critical security flaws and that AI models chose insecure coding methods 45% of the time when given a choice.
Part of the danger comes from what he called hallucinated dependencies: AI coding tools sometimes invent the name of a software package that does not exist, and attackers have started creating malicious packages under those exact names, waiting for unsuspecting code to pull them in. He cited a study finding that nearly 19.7% of AI-generated code samples reference at least one hallucinated package. AI-assisted code commits also leak hardcoded credentials, he said, at twice the rate of human-written code.
Third-party software is now involved in 48% of breaches, a 60% increase since 2021, which is why he urged labs to treat every new tool, including ones built in-house, as something that needs formal review. He described a fellow at his own institution who built an AI agent to interpret lab SOPs during on-call shifts, a clever pilot that had never been vetted. "Labs must vet all software through this process before using it internally," he said, "even if it's a great little tool that somebody's created."
From 'castle and moat' to zero trust
He also urged labs to abandon the old ‘castle and moat’ model of cybersecurity, in which a strong perimeter keeps attackers out but grants broad access to anyone already inside, an approach that breaks down once a single account is compromised. In its place, he recommended a zero-trust strategy in which "no one can be trusted" and every user, regardless of title, has to authenticate at every layer of the network. "I don't care if you're the CEO or if you're the mailroom person," he said. "You're going to have to authenticate into your systems no matter what."
He also warned against shadow AI, the use of personal or consumer AI accounts for institutional work, pointing to OpenClaw, an open-source AI automation platform that exploded in popularity in early 2026 before researchers discovered more than 1,000 unprotected gateways into it, prompting Microsoft to advise against running it on enterprise machines at all. Staff pasting patient data into consumer chatbots poses a similar risk, since institutions can't be sure how that data is stored or reused.
Cloud adoption and governance determine how safely labs can scale AI
On cloud adoption, he was direct about the numbers: Healthcare cloud computing is projected to quadruple by 2035, and 80% of health organizations already run at least one cloud-based application. At Mayo Clinic, a 10-year cloud partnership has moved nearly 90 petabytes of data into a virtual private cloud that only Mayo can access.
He was equally direct about governance, too often seen as a brake on innovation rather than what makes safe adoption possible. "Governance is what's gonna let you say yes to AI safely rather than say no out of ignorance," he said. His team built an internal framework called CARE, the Clinical AI Risk Evaluator, which maps AI development onto the same design, validation, and implementation phases labs already use for test development. He also described a low-, medium-, and high-autonomy scale for AI tools, from systems that simply draft suggestions for human review up to fully autonomous tools that act without oversight, the kind he said labs should generally avoid given the clinical stakes.
As a real-world example, he described a project in which off-the-shelf machine vision cameras were trained to spot uncapped or defective specimen tubes on an automation line, catching defects in under a second per plate with 100% sensitivity during validation. In the live Q&A, he added practical advice: check whether an institutional AI subscription already exists before defaulting to personal accounts, and expect cloud versus on-prem decisions to land somewhere in between. "The answer is it varies," he said. "It depends on your use case, what you're trying to do."
The throughline across his talk was consistent: innovation and security are not opposing goals, and labs that build governance in from the start will be the ones able to adopt AI and cloud technology with confidence rather than fear.
The full webinar is available to watch hereLinks
Related content
Tags
Frequently asked questions
Show frequently asked questions
What are the biggest AI risks facing clinical laboratories?
Clinical laboratories face several AI-related risks, including cybersecurity threats, AI-generated phishing attacks, vulnerable AI-written code, data privacy concerns, and insufficient governance frameworks. As AI adoption increases, laboratories must balance innovation with security and compliance.
How is AI changing cybersecurity threats in clinical laboratories?
AI enables attackers to create more convincing phishing emails, text messages, and voice scams. Advanced techniques such as deepfakes and voice cloning can make cyberattacks more difficult to detect, increasing risks for healthcare and laboratory organizations.
What is AI-generated code, and why is it a security concern?
AI-generated code is software written partially or entirely by artificial intelligence tools. Research has shown that AI-generated applications can contain security vulnerabilities, hallucinated software dependencies, and exposed credentials that may increase cybersecurity risks.
What is zero-trust security in healthcare laboratories?
Zero-trust security is a cybersecurity approach that assumes no user or device should be automatically trusted. Every user must continuously authenticate and verify access, reducing the risk of unauthorized access and cyberattacks within laboratory environments.
Why is governance important for laboratory AI adoption?
AI governance helps laboratories evaluate, validate, and monitor AI solutions before implementation. Effective governance reduces risk, supports regulatory compliance, and enables organizations to adopt AI technologies more safely and confidently.
Is cloud computing safe for clinical laboratories?
Cloud computing can be secure when properly configured. Many cloud-related breaches result from misconfigured environments rather than issues with the cloud platform itself. Strong security controls, access management, and governance are essential for safe cloud adoption.
What is shadow AI, and why should laboratories avoid it?
Shadow AI refers to employees using personal or unapproved AI tools for work-related tasks. This can create data security, privacy, and compliance risks, particularly when sensitive patient or laboratory information is shared with external AI platforms.
How can laboratories safely implement AI technologies?
Laboratories can safely implement AI by establishing governance frameworks, conducting cybersecurity reviews, validating AI tools before deployment, monitoring performance, and ensuring users receive appropriate training on AI risks and best practices.
How does AI support laboratory operations?
AI can improve laboratory efficiency through automation, image analysis, workflow optimization, decision support, quality management, and error detection. However, appropriate oversight and validation remain essential to ensure safe and reliable use.
What should laboratory leaders consider before adopting AI?
Laboratory leaders should assess cybersecurity risks, data privacy requirements, regulatory obligations, governance processes, integration needs, and the level of human oversight required before implementing AI solutions.